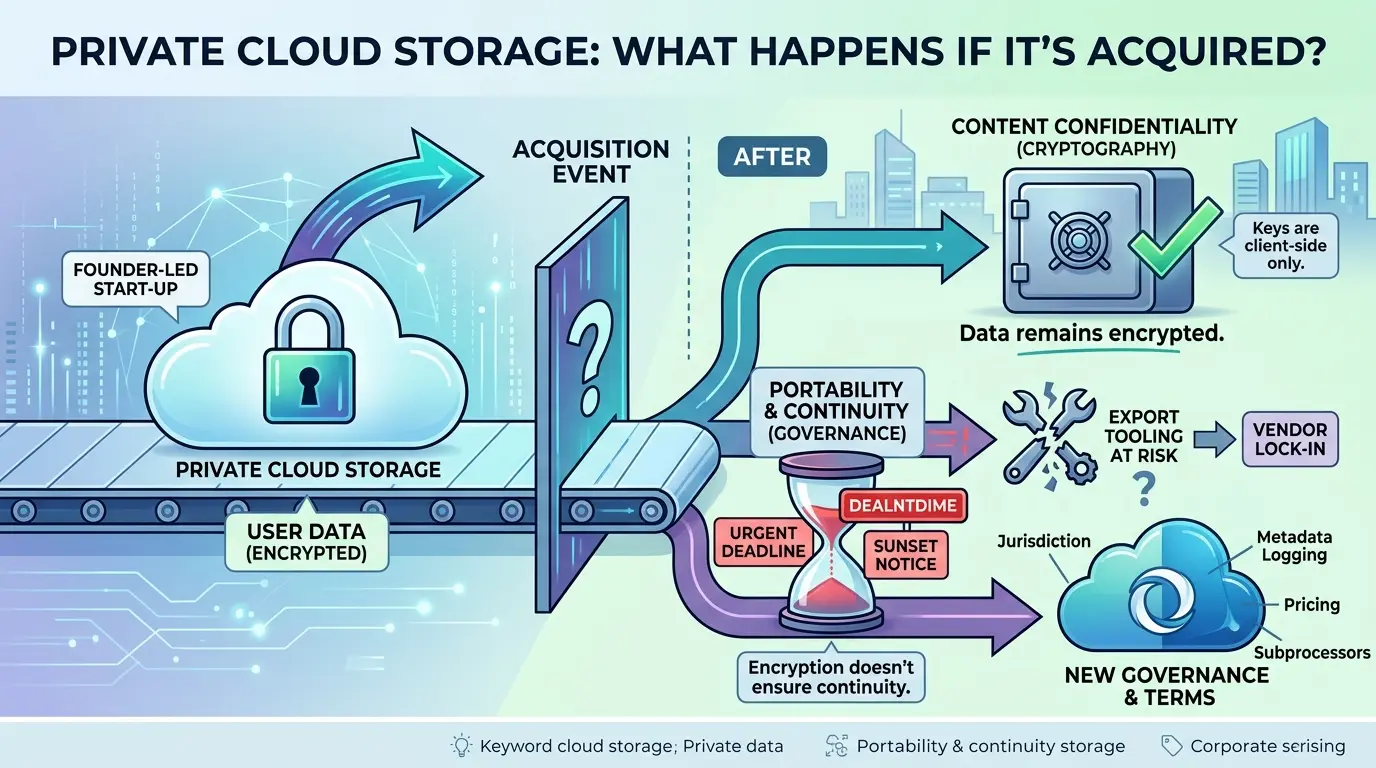

Encryption did not save Skiff users from a migration deadline.
That’s the uncomfortable fact sitting underneath every “best encrypted cloud storage” list published since February 2024. Skiff had genuinely strong end-to-end encryption. Its whitepaper described a client-side key model, an “honest but curious” server assumption, and a threat model that most competitors still haven’t matched on paper. None of that stopped the countdown clock that started the moment Notion announced the acquisition.
Mail, Pages, Calendar, and Drive went dark on 9 August 2024. Users spent that spring exporting MBOX files and requesting domain-transfer codes, not reading about how unbreakable their encryption was.
Here’s the part almost no comparison article mentions: this story isn’t over. Notion built a new email product, Notion Mail, largely from Skiff’s own team, launched it in April 2025, and marketed it as an AI-powered inbox. It does not use end-to-end encryption.
And as of this writing, Notion’s own help center confirms that Notion Mail itself is shutting down on 22 September 2026, roughly seventeen months after launch, for a completely different reason: the company says more than half its users had stopped opening the inbox and were letting AI agents handle email instead. For anyone who followed Skiff into Notion Mail, this is the second shutdown notice in under three years.
That second act is the real lesson of this article. A privacy provider’s acquisition is not primarily a cryptography problem. It’s a governance problem. The question that matters isn’t just “can the new owner read my files?” It’s “can I still authenticate, recover my account, export everything that matters, and trust whatever this company builds next?”
What this guide actually answers
Click any topic to expand or collapseImpact of acquisitions on encryption scope
What an acquisition can and cannot change about content that’s genuinely end-to-end encrypted.
Skiff to Notion Mail shutdown timeline
The complete, dated Skiff→Notion Mail→shutdown timeline, including the 2026 sequel most articles don’t know about yet.
Zero-knowledge vs. Encrypted at rest vs. E2EE
How “zero-knowledge,” “encrypted at rest,” and “end-to-end encrypted” actually differ—and why the difference decides what an acquirer inherits.
Six-surface acquisition risk framework
A six-surface framework for scoring acquisition risk before you commit important data to any provider.
Provider comparison matrix
Where Tresorit, Proton, Sync, pCloud, MEGA, Nextcloud, and Cryptomator sit on ownership history, key custody, and exit difficulty.
30-day exit readiness checklist
A practical, staged checklist for testing whether you could actually leave a provider in 30 days.
⚡ The 30-Second Verdict: Best Private Cloud Storage by Threat Model
Quick MatrixIf you need an immediate recommendation before diving into the legal, technical, and governance breakdown below, here is how the top private cloud storage options stack up against acquisition and vendor-lock-in risk:
The Short Answer: Acquisition Is Not Automatic Decryption
If a service genuinely encrypts your files on your device, and the provider never holds or can recover your decryption keys, a change in ownership does not by itself decrypt your existing files. That’s a real, defensible technical principle, but notice how many conditions are packed into it.
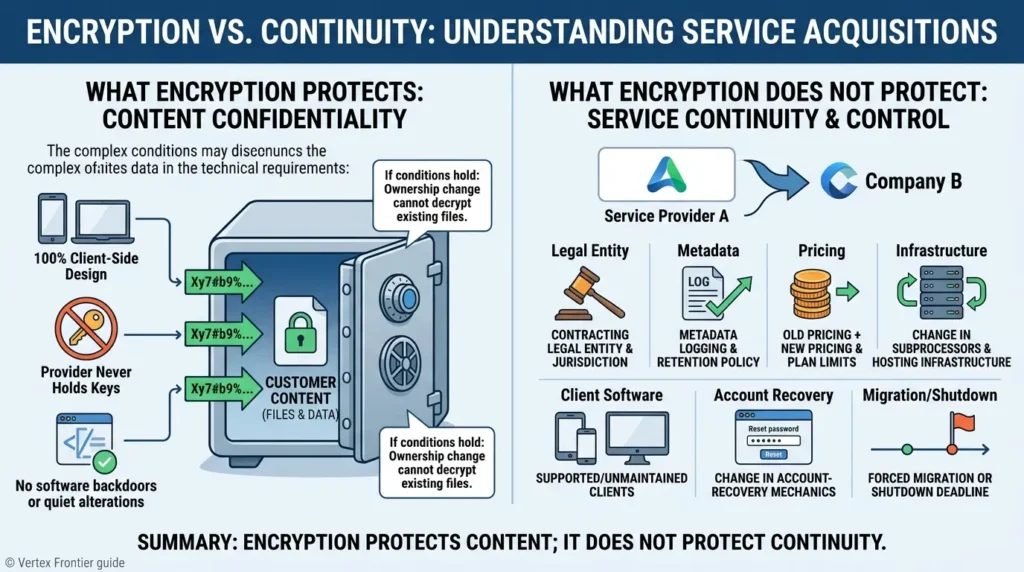
The design has to be genuinely client-side. The new owner can’t already control an authorized endpoint (your logged-in phone, for instance). The keys can’t have been escrowed or recoverable through a password-reset flow. And the client software you’re currently running can’t have been quietly altered to leak plaintext or freshly generated keys before the acquisition even closed.
Assuming all of that holds, here is what an acquirer typically can still do, without touching a single byte of your ciphertext: change the legal entity you’re contracting with, change which country’s courts and regulators apply, change subprocessors and infrastructure, change account-recovery mechanics, change what metadata gets logged and for how long, change pricing and plan limits, change which clients get maintained, change export tooling and its availability, and set a shutdown or migration deadline you didn’t choose.
None of that requires breaking your encryption. All of it can still upend your relationship with the service. This distinction, between content confidentiality and the continuity and control system wrapped around it, is the organizing idea for everything that follows. For a deeper technical breakdown of what encryption actually promises versus what it doesn’t, see Vertex Frontier’s guide to what end-to-end encryption does—and does not—protect.
In short: encryption protects content; it does not protect continuity.
What Happened to Skiff After Notion Acquired It: A Detailed Case Study
Skiff was founded in 2020 by Andrew Milich and Jason Ginsberg, and by late 2023 it had reportedly grown to close to two million users offering end-to-end-encrypted mail, documents, calendar, and drive storage, pitched directly at people who wanted an alternative to Google Workspace without Google’s data model. On 9 February 2024, Notion announced that Skiff was joining Notion.
What follows is a genuinely useful case study precisely because it isn’t a horror story about broken encryption. It’s a case study in exit mechanics.
| Date | Event | Confidence |
|---|---|---|
| 9 Feb 2024 | Notion announces Skiff is joining Notion. Initial notice: product suite closes after a six-month sunset. | High |
| 13 Feb 2024 | After user backlash, Skiff announces mail forwarding will run “through 2025, for one year going forward.” Contemporary reporting describes this as a shift from a six-month to a twelve-month sunset. | High for the update itself |
| 9 Aug 2024 | Mail, Pages, Calendar, and Drive are sunset. Automatic forwarding continues only for accounts that had enabled it before this date. | High (official term) |
| 9 Feb 2025 | The forwarding extension officially ends. | High as a promised date; medium for uninterrupted operation across every account |
| Apr 2025 | Notion launches Notion Mail, a Gmail client built largely by former Skiff engineers—without end-to-end encryption. | High |
| 25 Jun 2026 | Notion announces Notion Mail itself will shut down 22 September 2026, citing an “agent takeover” of email workflows. | High (confirmed on Notion’s own help page) |
| 22 Sep 2026 | Notion Mail shuts down. Any Notion-Mail-only data not exported by 21 September is permanently deleted. | High (official date) |
Resolving the “six months vs. twelve months” confusion
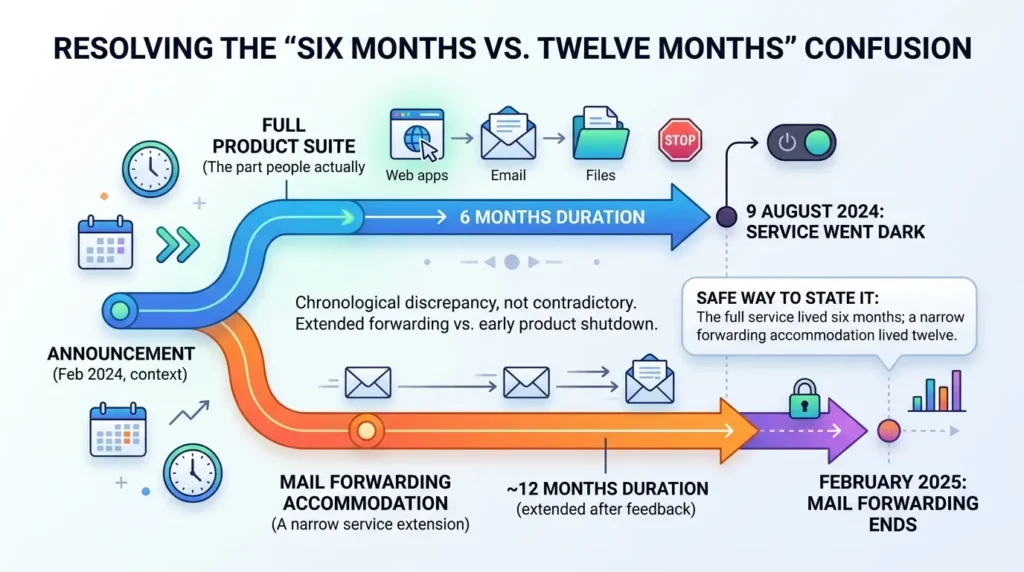
You’ll still see both numbers cited, and the discrepancy is chronological rather than contradictory. The original notice said six months. After feedback, Skiff extended mail forwarding to run through February 2025, about twelve months from the announcement.
But the product suite itself, the part people actually used, still went dark on the original six-month date, 9 August 2024. The safest way to state it: the full service lived six months; a narrow forwarding accommodation lived twelve.
What users actually had to do
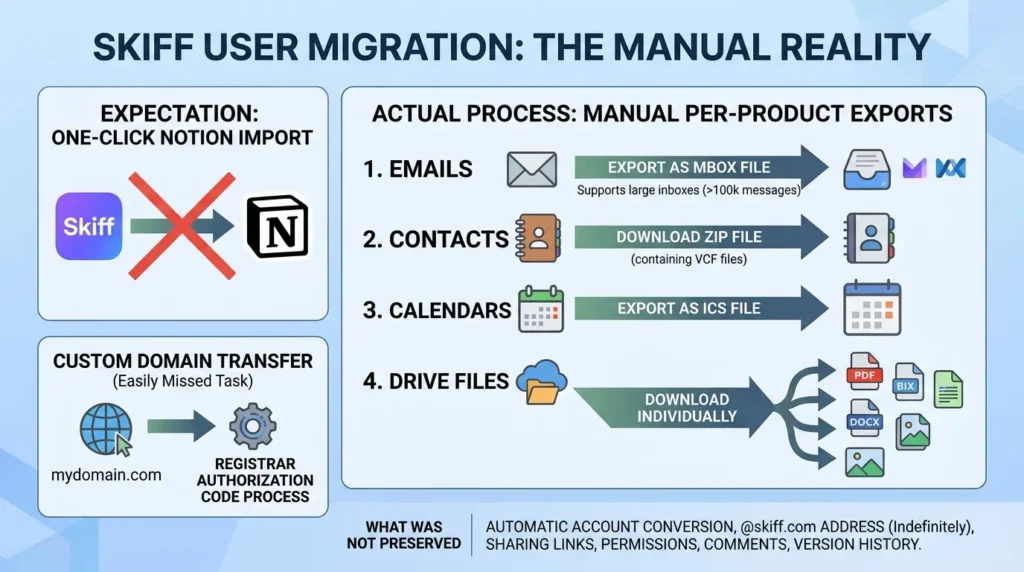
Skiff’s own migration FAQ stated that “all user data remains end-to-end encrypted” and that “accounts and data on Skiff will not be converted into Notion accounts.”
That statement is accurate as far as it goes, and it’s also narrower than it sounds. It tells you Skiff data wasn’t silently copied into an ordinary Notion account. It does not tell you whether Notion personnel had any administrative access to the underlying infrastructure, how backups were retained, or how deletion was verified, those questions remain unresolved in the public record.
In practice, migration meant manual, per-product exports: Proton’s contemporaneous migration guide and Mailfence’s independent instructions both describe the same workflow, mail exported as MBOX (Skiff’s own update said even inboxes over 100,000 messages could export as a single MBOX file), contacts as VCF files inside a ZIP, calendars as ICS, and Drive files downloaded individually.
Custom domains needed a separate transfer process through a registrar authorization code, which is a meaningfully different task from downloading files, and one users could easily miss.
What nobody could rely on: automatic account conversion, a one-click Notion import, indefinite preservation of a @skiff.com address, or a provider-to-provider transfer of sharing links, permissions, comments, or version history. One documented Reddit account describes a user who lost their skiff.com address, reported forwarding problems, and had difficulty getting support to help reset a dependent account, a genuine first-hand report, though a single account, not proof of a systemic failure across the user base.
The sequel nobody was tracking: Notion Mail’s own shutdown
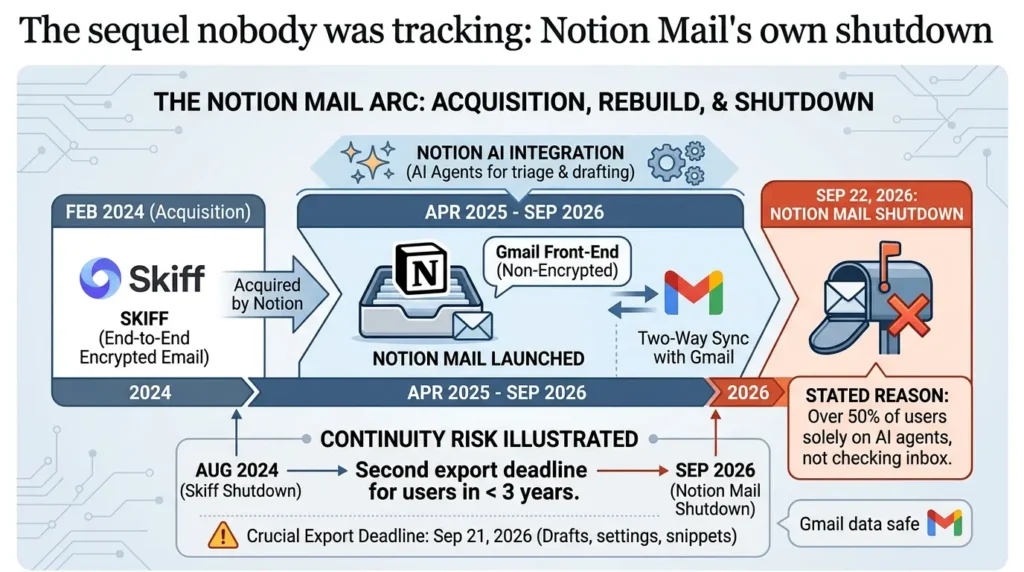
This is the update that most existing “what happened to Skiff” articles won’t have, because it’s recent enough to still be current news as this article is written. Notion didn’t simply let Skiff’s email concept die in August 2024. It rebuilt it, Notion Mail, staffed largely by former Skiff engineers, launched in April 2025 as a Gmail front-end with Notion’s AI layered on top. Critically, it dropped Skiff’s defining feature: Notion Mail was never end-to-end encrypted. It synced two ways with Gmail, meaning Google, not just Notion, had visibility into the same mail.
Seventeen months later, Notion killed that too. Per Notion’s own announcement, the shutdown lands on 22 September 2026, and the company’s stated reason has nothing to do with privacy, cost-cutting, or competitive pressure in the usual sense, it says more than half of Notion Mail’s users had already stopped opening the inbox and were letting AI agents triage, draft, and send on their behalf, so it’s “going all in on using agents to run your inbox.”
Drafts, scheduled emails, snippets, and auto-label rules need exporting by 21 September or they’re gone; actual email history is safe because it lived in Gmail the whole time. Organizations relying on HIPAA coverage were told to transition off by 30 June 2026, months ahead of the general deadline.
Step back and look at the full arc: an end-to-end-encrypted product got acquired, was rebuilt as a conventional Gmail client without that encryption, and less than a year and a half later got discontinued for an unrelated strategic reason. For anyone who migrated from Skiff to Notion Mail specifically because it felt like the closest thing left, this is the second export deadline in under three years, and a concrete illustration of exactly the continuity risk this article is about.
Encryption did not make Skiff portable by itself. Users still depended entirely on the provider to keep the lights on long enough to export, to ship a working export tool, and to honor a forwarding promise. Skiff’s cryptography was never the failure point. The absence of a durable exit path was.
What “Private Cloud Storage” Actually Means
“Private,” “encrypted,” “zero-knowledge,” and “end-to-end encrypted” get used almost interchangeably in marketing copy. They describe genuinely different trust boundaries, and the difference determines exactly what an acquirer inherits.
Encryption in transit vs. encryption at rest
Encryption in transit protects data as it moves between your device and the provider’s server, this is what TLS does. RFC 8446, the current TLS standard, provides confidentiality and integrity for traffic between two communicating endpoints; it says nothing about what happens to that data the moment it arrives at the server and TLS terminates. “Encrypted in transit” is not evidence of end-to-end encryption, it just means nobody sniffed your Wi-Fi.
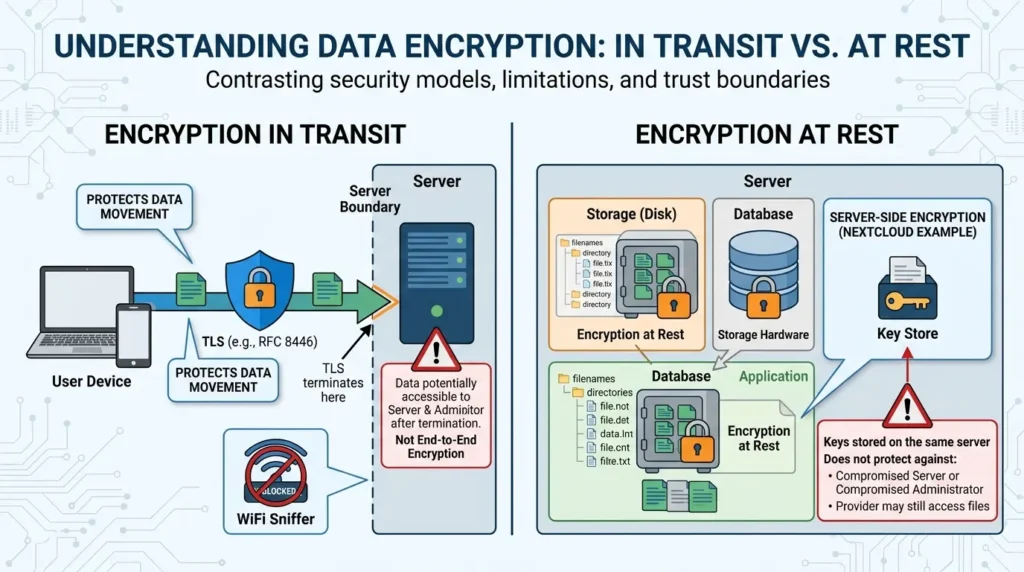
Encryption at rest protects data sitting on a disk or in a database. It can be implemented at the storage-hardware level, the database level, or the application level, and each has a different trust boundary. Nextcloud’s own administration documentation is refreshingly direct about the limits here: its server-side encryption performs encryption and decryption on the server, stores the keys on that server, and explicitly does not protect against a compromised server or a compromised administrator.
Filenames and directory structures aren’t encrypted either. “Encrypted at rest” tells you the provider took a reasonable security step. It does not tell you the provider can’t read your files.
Client-side encryption and end-to-end encryption (E2EE)
End-to-end encryption means content is encrypted on one endpoint and only decrypted on another endpoint the sender trusts, with no intermediate party, including the service provider, able to decrypt it in between. The defensible test isn’t the marketing label; it’s operational: who can decrypt content, filenames, thumbnails, previews, search indexes, sharing keys, and backups? Where are keys generated, and can any support process recover them?
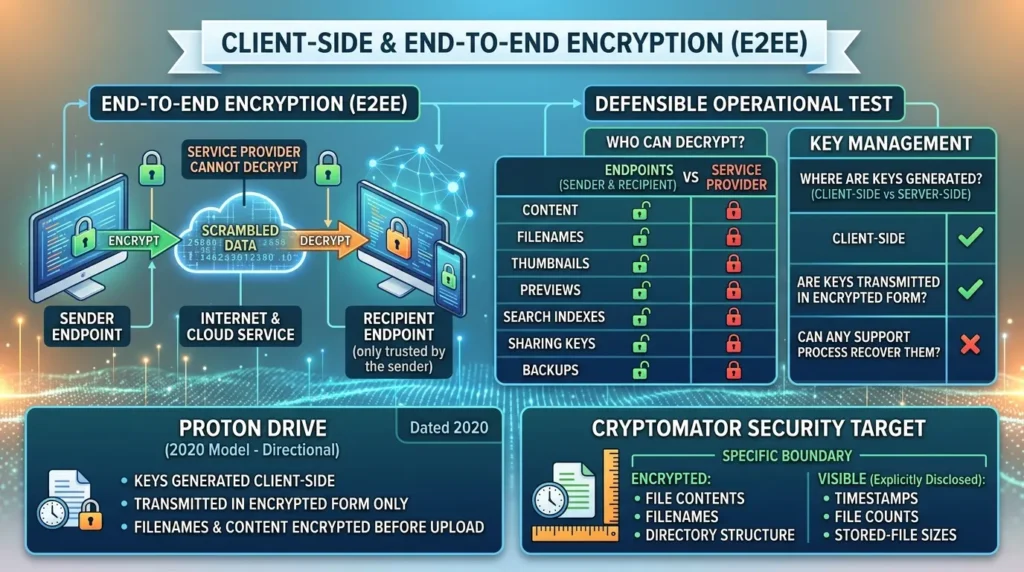
Proton’s published Drive security model, for example, states that encryption keys are generated client-side and only ever transmitted in encrypted form, with filenames and content both encrypted before upload, though that documentation is dated 2020, so treat it as directional rather than a guarantee of every current feature’s behavior.
Cryptomator’s Security Target is more specific about the boundary: it documents encryption of file contents, filenames, and directory structure, while explicitly disclosing that timestamps, file counts, and stored-file sizes remain visible.
Zero-knowledge is a marketing term, not a certification
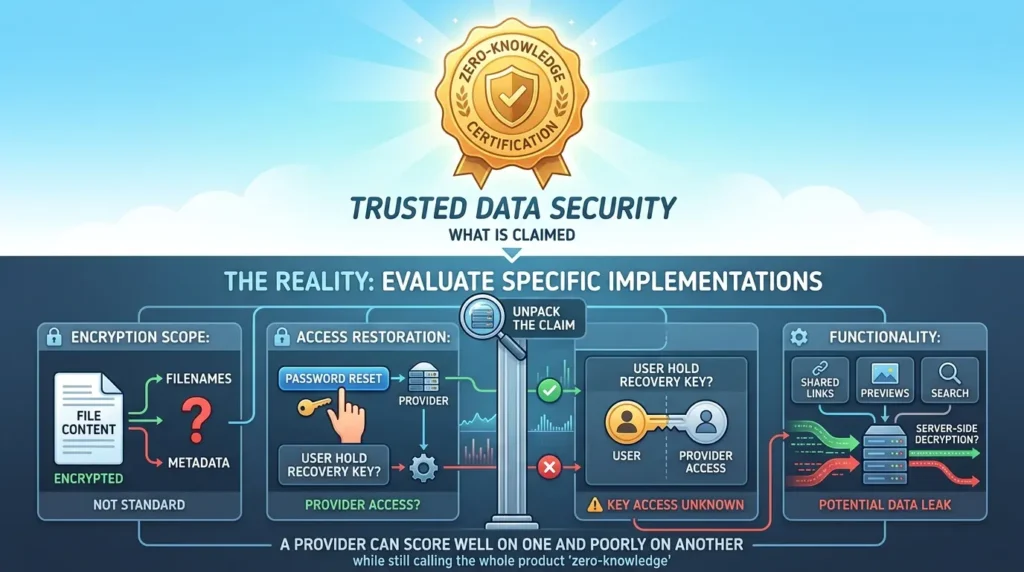
“Zero-knowledge” has no single standardized technical meaning. Treat it as a claim to unpack, not a badge to trust. The unpacking questions are always the same: Does it cover file content only, or also filenames and metadata? Can a password reset restore access, and if so, how? Is there a recovery key, and who holds it? Do shared links, previews, or search functions require server-side decryption at any point? A provider can score well on one of these and poorly on another while still calling the whole product “zero-knowledge.”
Metadata: the part encryption usually doesn’t touch
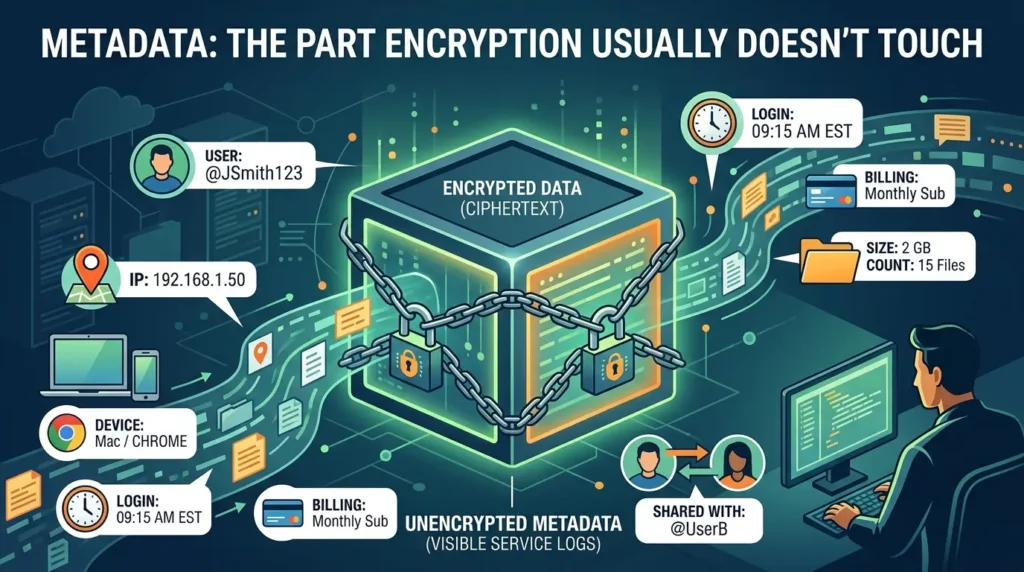
Even a well-implemented E2EE system typically leaves a trail: account identity, IP address, device and browser information, login timestamps, billing data, API request logs, object sizes, timestamps, object counts, and sharing events. None of that requires decrypting your files, it’s generated by the act of using the service. An acquirer who can’t touch your ciphertext can often still see who you are, when you’re active, roughly how much data you store, and who you share it with.
Key custody and recovery: the trade-off nobody wants to name
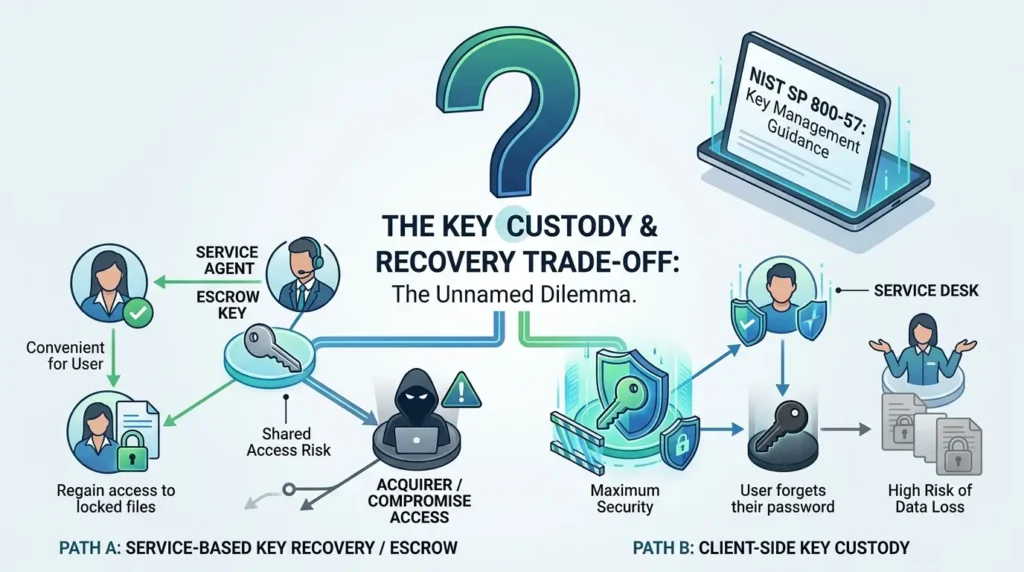
NIST’s guidance on key management (SP 800-57) treats cryptographic keys as an operational asset across their entire lifecycle, generation, use, backup, recovery, and destruction, and separately defines key escrow as a third party holding a key, or part of one, so it can be recovered under specified conditions.
This creates an unavoidable trade-off: a service that can reset your password and still decrypt your old files necessarily has some key-recovery mechanism, and that mechanism is a smaller version of the exact access an acquirer might one day inherit.
Conversely, a genuinely unrecoverable forgotten password, like Tresorit’s, whose support documentation states passwords aren’t stored on its servers and can’t be recovered except through specific logged-in-device or business-admin paths, is often a deliberate consequence of real client-side key custody, not a design flaw.
What Actually Changes When a Privacy Provider Is Acquired
Ownership and the legal counterparty
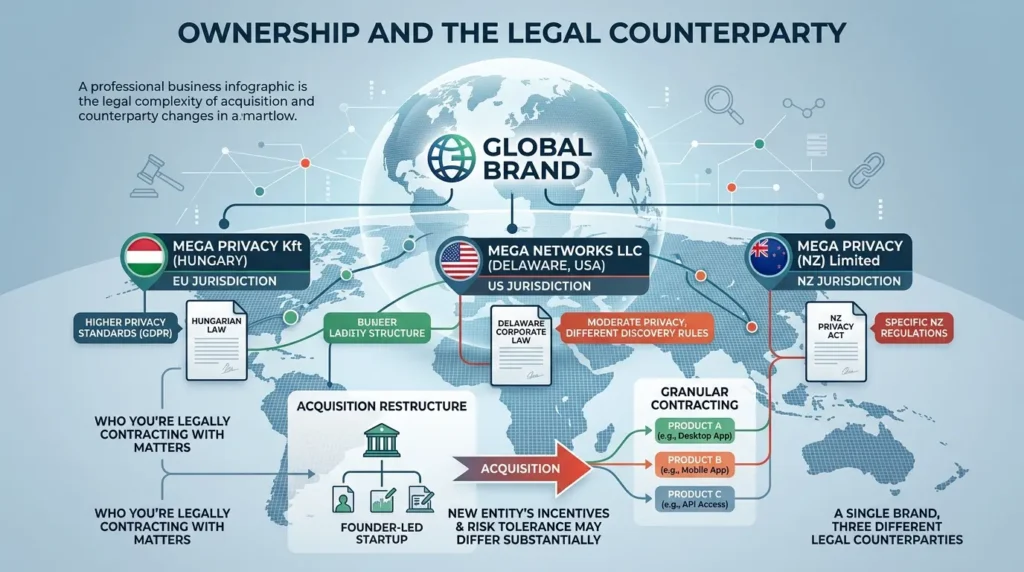
An acquisition changes who you’re legally contracting with, which matters more than it sounds, because that new entity’s incentives, risk tolerance, and jurisdiction may differ substantially from the founder-led startup you originally trusted.
MEGA’s current terms illustrate how granular this can get: depending on which product or access route you use, you may be contracting with MEGA Privacy Kft in Hungary, MEGA Networks LLC in Delaware, or MEGA Privacy (NZ) Limited, three different legal entities, three different governing laws, under a single consumer brand. A single acquisition can restructure this without changing a single line of your files.
Jurisdiction is not the same as data-center location
It’s tempting to assume that a provider storing files in a privacy-friendly country is safe from other jurisdictions’ legal reach. That’s not how it works. The U.S. Department of Justice describes the CLOUD Act as enabling access to data held by U.S.-based providers “wherever it happens to be located.”
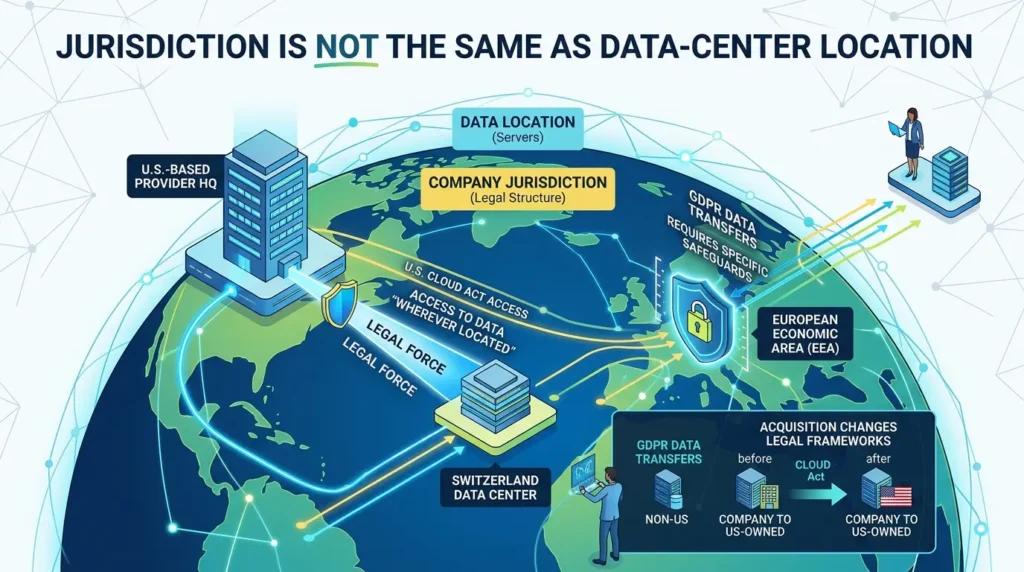
Separately, the EDPB’s guidance on international data transfers explains that GDPR governs transfers outside the EEA and can require specific safeguards. Neither of these guarantees a particular outcome for any specific request, but both establish that the company’s jurisdiction and legal structure matter independently of where the servers physically sit. An acquisition that changes the parent company’s home country can change which of these frameworks apply, even if not a single server moves.
Terms, pricing, and retention
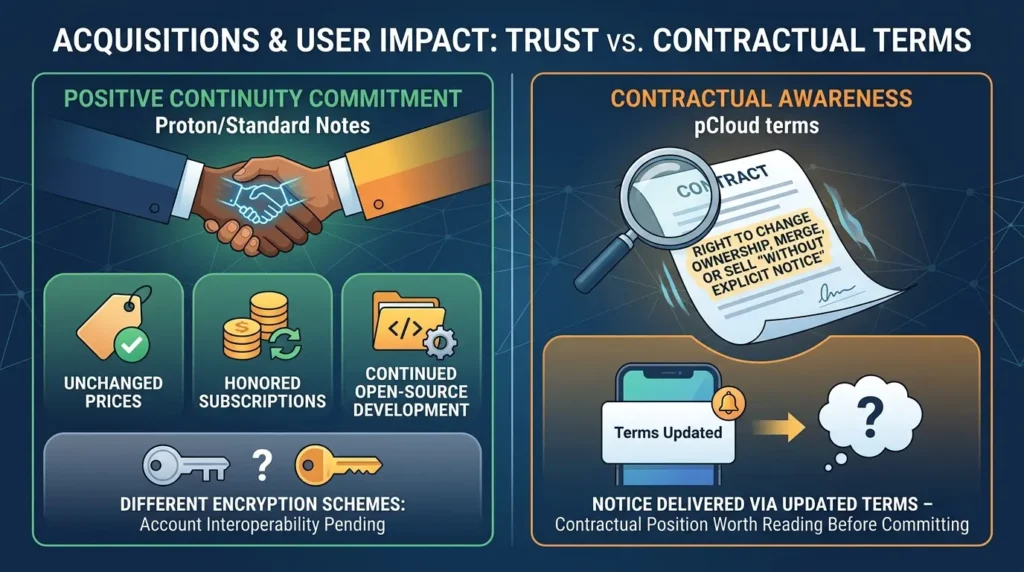
A new owner can revise plan limits, acceptable-use terms, or pricing even when the underlying encryption is untouched. This isn’t hypothetical pessimism, it cuts both ways. When Proton acquired Standard Notes in 2024, it explicitly promised unchanged prices, honored existing subscriptions, and continued open-source development, a genuine continuity commitment.
But note what that deal is not: it’s an adjacent privacy-ecosystem acquisition, not a Proton Drive acquisition, and TechCrunch’s contemporaneous reporting noted that Standard Notes and Proton’s other products used different encryption schemes, with account interoperability described as a future possibility rather than something already delivered. A positive continuity promise and an unresolved integration question can be true at the same time.
Contrast that with pCloud’s terms, which explicitly reserve the right to change ownership, merge, or sell “without explicit notice,” with notice delivered simply by updating the published Terms. That’s not evidence anything bad has happened at pCloud, no ownership event has been publicly verified, but it’s a contractual position worth reading before you commit, not after.
Infrastructure, subprocessors, and the encryption implementation
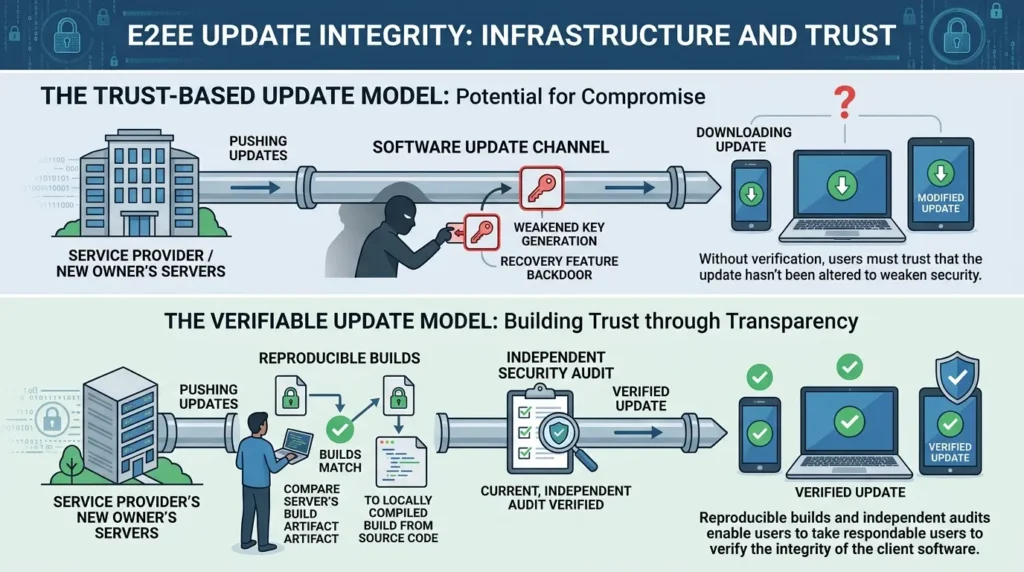
Even genuine E2EE has an update channel. Whoever controls the client software you download controls, in principle, what that software does going forward, including whether a future update quietly weakens key generation or adds a “helpful” recovery feature that widens who can decrypt your data.
This is a residual threat to name honestly, not evidence of intent by any specific company: unless a provider publishes reproducible builds or has undergone independent, current audits, “the update channel can’t be changed by a new owner” isn’t something you can verify, it’s something you’re trusting.
Account recovery and metadata practices
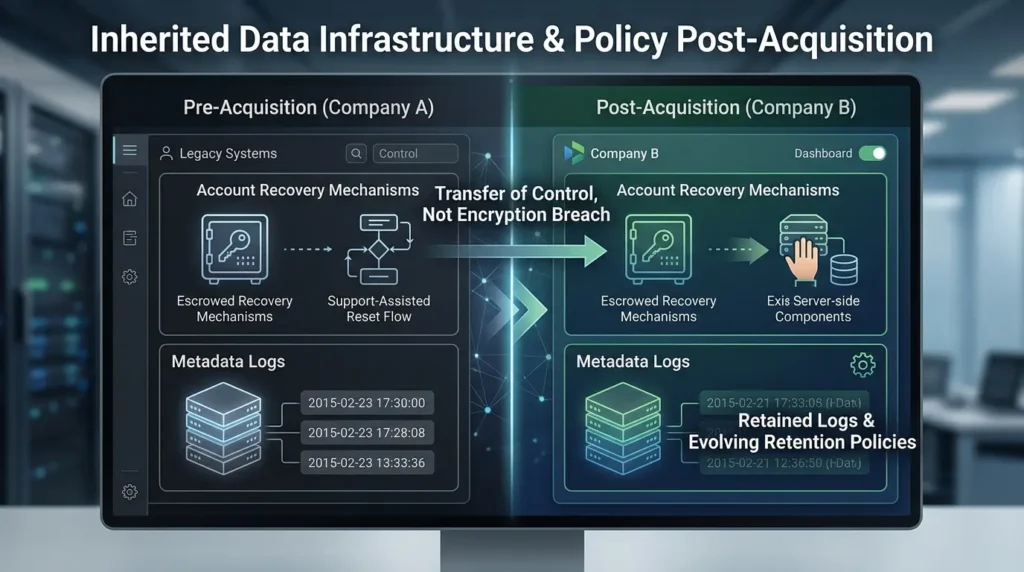
Acquirers inherit, and can change, whatever recovery mechanism existed before the deal closed. If that mechanism already involves some server-side capability (a support-assisted reset, an escrowed recovery key), the acquisition doesn’t need to break your encryption to expand what’s accessible; it just needs to change who operates that existing mechanism.
The same logic applies to metadata retention: nothing about an acquisition automatically deletes old logs, and a new owner may have different incentives about how long to keep them or what to do with them.
Export tooling and shutdown policy
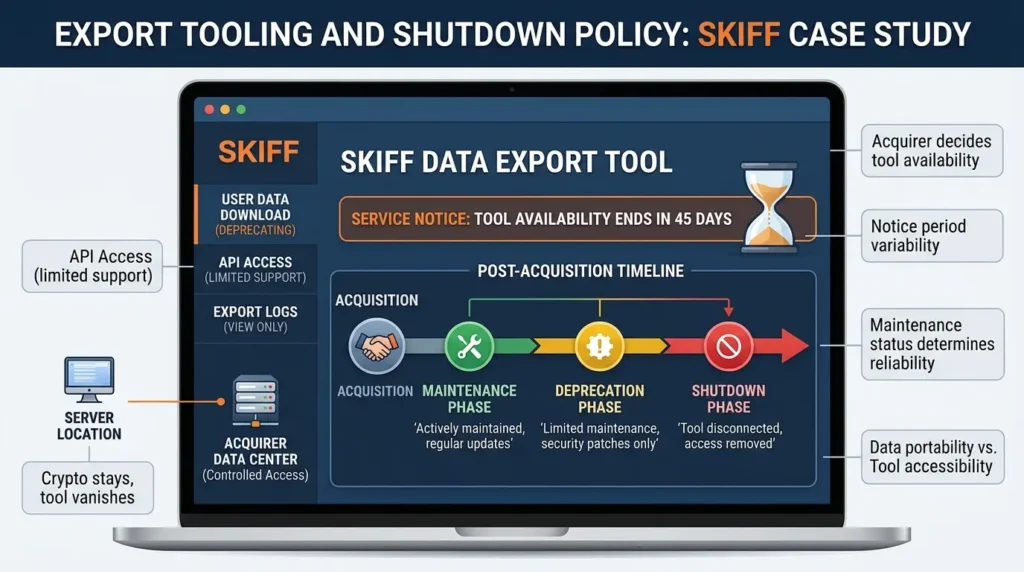
This is where the Skiff case study becomes most directly useful. The acquirer decides how long an export tool stays available, whether it’s actively maintained, and how much notice you get before it disappears. A “you can always export your data” claim is only as good as the tool that exists on the day you actually need it, and that tool’s continued existence is precisely the kind of thing an acquisition can change without touching any cryptography at all.
In one line: an acquisition can leave your ciphertext completely untouched while changing almost everything else that determines whether you can keep using, trust, or leave the service.
Evaluating Private Cloud Storage: A Six-Surface Acquisition Risk Framework
Most reviews collapse “privacy” into a single score or a marketing badge. That flattens a genuinely multi-dimensional problem. A more useful model treats acquisition risk as six separate, independently scoreable surfaces.
| Surface | Core question | What an acquisition can do |
|---|---|---|
| Content confidentiality | Can the operator decrypt file contents under the actual, current design? | Historical ciphertext may stay protected if keys are genuinely client-only; future clients or recovery changes can move that boundary. |
| Metadata confidentiality | What account, network, timing, and billing data is visible regardless of content encryption? | The buyer can inherit or actively change logging, telemetry, and retention practices. |
| Identity continuity | Can you keep your addresses, domains, aliases, and forwarding? | A shutdown or consolidation can break identity even when files export cleanly—exactly what happened to some Skiff users. |
| Availability and recovery | Can you access your data during and after a transition? | The buyer sets support levels, deletion timelines, and how long export tools stay maintained. |
| Legal and governance control | Who is the counterparty, and which laws and processors apply? | Corporate control changes can shift jurisdiction and contractual context without any notice requirement guaranteed in every case. |
| Future software trust | Can future client updates change what’s exposed? | The buyer controls future releases and signing infrastructure unless independent, reproducible builds exist. |
A provider can score strongly on content confidentiality while scoring poorly on identity continuity or portability, Skiff is the textbook case. Score all six surfaces separately before trusting any single “zero-knowledge” or “private” label to cover the whole picture.
Private Cloud Storage Providers Compared
Before the table, one framing point matters: this isn’t a ranking. It’s a record of what’s actually documented about each provider’s ownership history, encryption model, and exit friction, alongside honest gaps where the evidence doesn’t support a claim.
Three broad architectures are worth distinguishing first, because they carry structurally different acquisition risk:
- Managed hosted encrypted storage (Proton Drive, Tresorit, Sync, pCloud, MEGA), a vendor operates the service and promises client-side or E2EE protection. You depend on that vendor’s continuity and goodwill for export access.
- Self-hosted or independently hosted software (Nextcloud), you or your chosen host operates the infrastructure, trading vendor dependence for direct maintenance, patching, and backup responsibility. See Vertex Frontier’s take on why local control is not the same as automatic security, the same principle applies to self-hosted storage.
- A client-side encryption layer over ordinary storage (Cryptomator), you encrypt a vault yourself before it ever reaches a storage provider, which reduces dependence on that provider’s own cryptographic implementation and makes the encrypted vault itself more portable between backends.
| Provider | Ownership event | Who controls keys? | Main continuity risk | Best fit |
|---|---|---|---|---|
| Tresorit | Swiss Post acquired a majority stake, 2021 | User-side, per vendor’s E2EE claim | Continuity promise made publicly; no independent post-deal audit found | Teams wanting E2EE with an enterprise support layer |
| Proton Drive | No Drive-specific acquisition; Proton acquired Standard Notes (adjacent product) in 2024 | User-side, per Proton’s model (2020 documentation) | Cross-product integration can raise portability questions, as seen with Standard Notes’ different encryption scheme | Users already in the Proton ecosystem |
| Sync.com | No verified event found | User-side; provider states it cannot reset lost passwords | Privacy policy explicitly permits disclosure in a future merger/sale | Canadian-jurisdiction preference |
| pCloud | No verified event; terms explicitly allow future ownership change | User-side only for the paid “Crypto” add-on, not ordinary storage | Contract already anticipates a sale with limited notice obligation | Users who specifically enable Crypto—not a blanket zero-knowledge claim |
| MEGA | Kim Dotcom resigned as director, 2013 (management change, not a verified acquisition) | User-side, per published terms | Multiple contracting entities (Hungary, Delaware, New Zealand) depending on product/access route | Users comfortable tracking which legal entity applies to their plan |
| ownCloud/DRACOON → Kiteworks | Merger into US-based Kiteworks, 2023 | Customer-controlled key claims per Kiteworks | Nextcloud (a competitor) publicly warned of forced migration for overlapping products—read as commentary, not neutral evidence | Enterprise buyers already evaluating Kiteworks directly |
| Boxcryptor → Dropbox | Dropbox acquired key assets, 2022; original service later discontinued (31 Dec 2025) | Was user-side; service no longer operates | The strongest documented case of asset acquisition breaking service continuity—users had to decrypt/re-encrypt into a new vault format | Historical cautionary example |
| Wuala (LaCie/Seagate) | Shut down 2015; read-only period, then deletion | Was user-side; irrelevant after shutdown | Clearest precedent that encryption guarantees nothing about post-shutdown data access | Historical cautionary example |
| Nextcloud (self-hosted) | Software/ecosystem, not a single company—no centralized hosting event applies | Depends entirely on your deployment; server-side encryption does not protect against a compromised admin | Maintenance, backup, and upgrade risk shifts to whoever operates it—including you | Technical users willing to own operations |
| Cryptomator (encryption layer) | No event; not a hosted service | User-side by design; the vault can sit on any backend | Reduces storage-vendor risk but exposes timestamps, file counts, and sizes; doesn’t solve endpoint compromise or key loss | Anyone who wants portability independent of the underlying storage provider |
Two important caveats belong here, not buried in a footnote:
- First, “no verified event found” for Sync.com, pCloud, or Cryptomator is an explicit absence of evidence in publicly reviewed sources, not proof that no private transaction, investment, or restructuring has ever occurred.
- Second, SpiderOak received a strategic investment from Accenture Ventures in 2023; the public record describes this as an investment, not a change of control, and it shouldn’t be cited as an acquisition.
The providers with the cleanest documented continuity stories (Tresorit, Proton/Standard Notes) are also the ones that were most transparent about the transaction publicly. That’s a pattern worth weighting when you’re evaluating a provider you’re less familiar with.
SaaS Privacy Storage vs. Self-Hosted: The Trade-off Nobody States Plainly
Here’s the framing that gets lost in most “self-host everything” advocacy: self-hosting doesn’t eliminate acquisition risk. It transfers a different set of risks onto you.
A managed encrypted provider reduces your patching burden, gives you a support line, and typically ships a more polished client, at the cost of vendor dependence and continuity risk exactly like Skiff’s.
Self-hosting removes the vendor-continuity dependence but makes you responsible for security patching, backup integrity, disaster recovery, and upgrade safety. One Reddit user described a self-hosted Nextcloud upgrade that damaged their installation badly enough that they considered re-uploading 300 GB from scratch, a single documented account, not a verdict on Nextcloud generally, but a real illustration of where the operational burden actually lands once you own the infrastructure.
For a concrete sense of what that operational commitment looks like in practice, see Vertex Frontier’s guide on the operational cost of self-hosting and the companion piece on why production self-hosting requires more than installing software.
The balanced conclusion isn’t “SaaS bad” or “self-hosting safe.” It’s that both models carry real risk, just distributed differently:
| Risk | Managed SaaS provider | Self-hosted |
|---|---|---|
| Acquisition/shutdown risk | Real—you depend on the vendor’s continued existence | Effectively removed for the storage layer itself |
| Security patching | Vendor’s responsibility | Yours, on a schedule you set (or forget to set) |
| Backup and restore testing | Vendor-dependent; you should still keep an independent copy | Entirely yours—including remembering to test a real restore |
| Support during a crisis | Available, quality varies | Whatever community or paid support you’ve arranged |
Common Mistakes When Choosing a Private Cloud Storage Provider
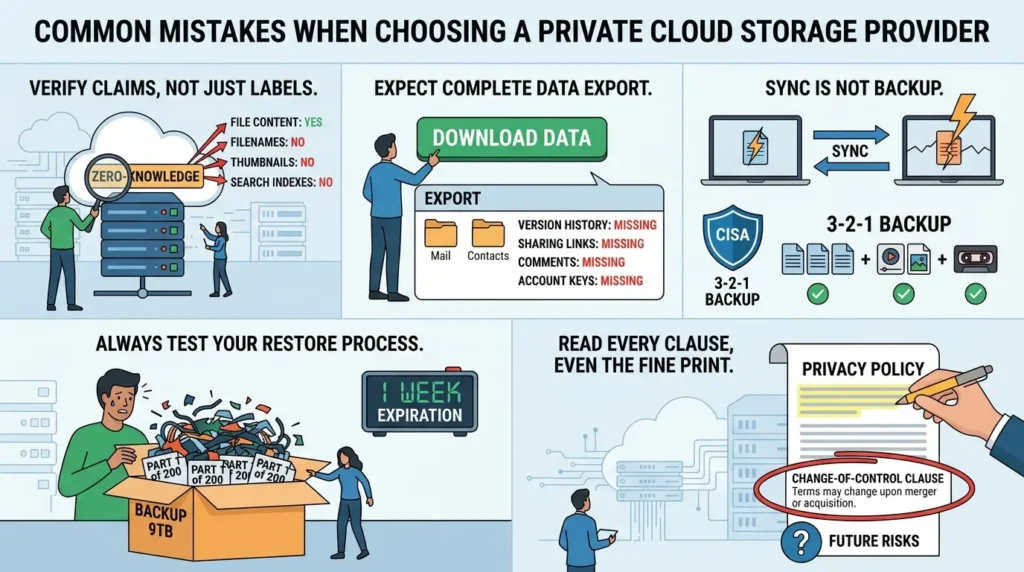
Treating “zero-knowledge” as a single fact instead of a set of claims to verify.
As covered above, the label can be true for file content and false for filenames, thumbnails, or search indexes, all in the same product.
Assuming “download your data” equals a complete export
A generic download button rarely covers version history, sharing-link permissions, comments, or account-level keys. Skiff’s export was real and functional for mail, contacts, calendars, and files, but it did not preserve sharing links, permissions, or collaboration state, because those aren’t just bytes; they’re relationships between accounts.
Confusing sync with backup
A synced folder that mirrors changes across devices will just as faithfully mirror a ransomware encryption or an accidental deletion. CISA’s guidance on backing up business data recommends the 3-2-1 approach, three copies, two different media, one offline, specifically because sync alone doesn’t satisfy it.
Never testing a restore
An export you’ve never actually tried to reopen isn’t a verified backup; it’s an assumption. A DataHoarder thread describing a 9 TB Google Takeout export documents hundreds of 50 GB archive parts, one-week download-link expirations, and inconsistent collection behavior, a vivid illustration that a nominally available export can still be an operational project, not a five-minute task, at real scale.
Reading the privacy policy but skipping the change-of-control clause
Sync.com’s and pCloud’s terms both explicitly anticipate a future merger or ownership change. That single clause tells you more about your realistic long-term exposure than most of the marketing copy above it.
A Practical Acquisition-Risk Checklist
- Read the change-of-control language in the terms and privacy policy, not just the marketing page.
- Check what export formats exist, and actually run a small export before you trust the service with anything important.
- Confirm whether an API, WebDAV, or S3-compatible endpoint is generally available—not waitlisted or plan-restricted.
- Identify the account-recovery trade-off: what happens if you forget your password, and does that answer worry you?
- Note the contracting entity and governing jurisdiction, not just the country the marketing page emphasizes.
- Keep an independent backup outside the provider—local, a second provider, or both.
- Periodically test a real restore, not just a file download.
- Avoid storing the only copy of anything irreplaceable in a single account.
- Watch for ownership, pricing, or terms-of-service change notices—don’t assume “no news” means “no change.”
- Download and verify a fresh export immediately—don’t wait for the final shutdown date, which is exactly what caught some Skiff and Notion Mail users off guard.
- Re-read the new terms and privacy policy for jurisdiction, subprocessor, or recovery-policy changes.
- Inventory every identity that depends on this provider: email addresses, aliases, domains, forwarding rules, calendars, and any account that uses this address for password recovery elsewhere.
- Document your migration as you go, and verify completeness against the object types you actually care about—not just “did the download finish.”
Before and After: What Exit-Readiness Actually Changes
Before treating excitability as a feature: You picked a provider based on its encryption claims and interface. Your only copy of important files sits in one account. You’ve never opened the export tool. If the provider announced a shutdown tomorrow, your first action would be panic, not migration, exactly the position many Skiff users found themselves in in February 2024.
After treating excitability as a feature: You know your export formats and have tested them on a small scale. You maintain an independent backup that doesn’t depend on the provider staying in business. You’ve inventoried which of your identities, email addresses, domains, recovery channels, depend on this specific provider. If an acquisition is announced, your first action is executing a plan you already understand, not discovering one under deadline pressure.
The technical protection, genuine end-to-end encryption, doesn’t change between these two states. What changes is whether an ownership event is a manageable inconvenience or a genuine crisis.
Conclusion: A Privacy Provider Is Also a Governance Dependency
Choose private cloud storage not only for how well it hides your files from the provider today, but for how safely you could replace that provider tomorrow. Keep independent keys and copies. Test a real restore, not just a download. Own the identities that matter, domains, aliases, recovery addresses, rather than renting them from a single company.
Understand exactly where the metadata boundary sits in whatever product you choose. And treat news of an acquisition as a prompt to re-check software, terms, jurisdiction, recovery mechanics, and export tooling, not as proof that the encryption you were promised has automatically failed.
Skiff’s encryption was never broken. Notion Mail’s shutdown, just over a week away as this article goes to press, isn’t a cryptographic failure either. Both are governance events wearing a technology story’s clothes. The providers worth trusting with your most important data are the ones that make leaving easy enough that you never actually have to.
Frequently Asked Questions
What happens to my files if my cloud storage provider is acquired?
If your files are genuinely end-to-end encrypted with keys the provider never held, an acquisition doesn’t by itself decrypt existing content. It can still change the legal entity you’re contracting with, jurisdiction, metadata practices, account recovery, pricing, and how long export tools remain available—all without touching your ciphertext.
Can a new owner read files protected by end-to-end encryption?
Not automatically, and only under specific conditions: the encryption must be genuinely client-side, the new owner must not already control an authorized endpoint, and the keys must never have been escrowed or recoverable. If any of those conditions doesn’t hold—for example, if the service can already reset your password and restore file access—the acquisition question becomes secondary to a pre-existing key-custody gap.
What happened to Skiff after Notion acquired it?
Notion announced the acquisition on 9 February 2024. Skiff’s Mail, Pages, Calendar, and Drive services were sunset on 9 August 2024, with automatic mail forwarding continuing only for accounts that enabled it, through 9 February 2025. Accounts were not converted into Notion accounts—users had to manually export mail (as MBOX/EML), contacts (VCF), calendars (ICS), and Drive files, and separately transfer any custom domains. Notion later built Notion Mail from much of the Skiff team, launched it in April 2025 without end-to-end encryption, and is shutting that product down as well on 22 September 2026.
What’s the difference between encryption at rest, client-side encryption, and end-to-end encryption?
Encryption at rest protects data sitting on a server’s disk or database but typically leaves the provider holding the keys, meaning it can still read your files. Client-side encryption means your device encrypts data before it ever reaches the provider. End-to-end encryption specifically means only the sender and intended recipient—not any intermediate server—can decrypt the content. The practical test isn’t the label; it’s whether the provider can technically produce plaintext under any documented recovery or support process.
What does “zero-knowledge” actually hide from a cloud provider?
It depends entirely on the specific product—”zero-knowledge” has no single standardized meaning. Some implementations hide file content only; others also hide filenames and folder structure. Nearly all leave some metadata visible: account identity, IP address, login timestamps, file sizes, and sharing activity. Before trusting the label, ask specifically what it covers for the exact feature you plan to use.
Is a second cloud copy the same as a backup?
No. A synced second copy mirrors changes automatically, including accidental deletions or ransomware encryption. A genuine backup is a separate, independently restorable copy—ideally following the 3-2-1 pattern CISA recommends: three copies, on two different media, with one stored offline. Sync alone doesn’t satisfy that standard.
Is self-hosted cloud storage safer than a managed encrypted provider?
It’s differently risky, not simply safer. Self-hosting removes vendor-continuity dependence—there’s no company to be acquired or shut down out from under you—but it transfers patching, backup integrity, and disaster-recovery responsibility onto you or your chosen operator. Community reports of damaged self-hosted upgrades show this operational burden is real, not theoretical. Managed providers reduce that burden while reintroducing vendor dependence.
Does an acquisition legally require my consent as a customer?
There’s no universal rule requiring customer consent for a corporate acquisition or change of control—this depends on the specific terms of service, applicable consumer-protection law, and jurisdiction. Many providers’ terms, including Sync.com’s and pCloud’s, explicitly anticipate and permit disclosure or transfer of customer data in connection with a future merger or sale. This is not legal advice; check the current terms for the specific provider and jurisdiction that applies to you.

Was this article helpful?
[…] This is the contrarian point: the strongest cryptography can be weakened by ordinary product decisions long before anyone breaks the math. And the most consequential product decision of all is a change in ownership, see what actually happens when a private cloud storage provider gets acquired. […]
[…] Skiff — whose shutdown after Notion’s acquisition is the case study we dissect in our private cloud storage acquisition risk guide) are mentioned briefly later, but these four form the comparison because they’re architecturally […]
[…] This is the same trade-off that exists for cloud storage: you either accept a vendor's acquisition risk or you accept the maintenance burden of self-hosting. We mapped both sides, including a six-surface acquisition-risk framework and when self-hosted Nextcloud actually wins, in our private cloud storage comparison. […]
[…] service itself when the company gets acquired. We explored that governance dimension in depth for private cloud storage, the same logic applies […]